Integrate Security. Start Strong.
Empower your developers with the essential resources, documentation, and tooling required to embed robust application security throughout the entire software development lifecycle (SDLC).
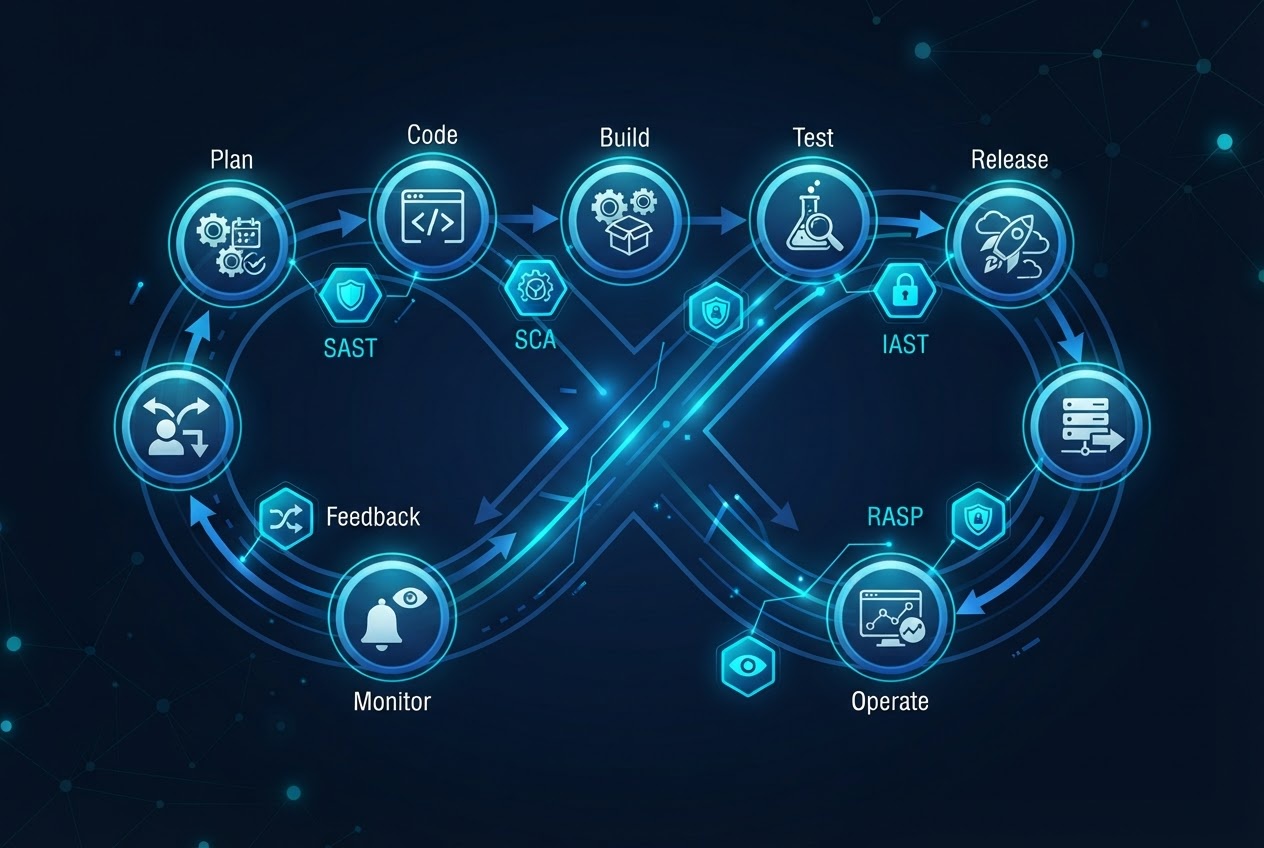
Shift Left Strategy
Foundational Pillars of Secure Development
CI/CD Security Automation
Automate Static Analysis (SAST), Dynamic Analysis (DAST), and Software Composition Analysis (SCA) seamlessly within your continuous integration pipelines.
Secure Coding Practices
Comprehensive guides for mitigating application vulnerabilities in modern frameworks (e.g., cross-site scripting, injection flaws, insecure deserialization).
Proactive Vulnerability
Tools and workflows for continuous vulnerability assessment, clear reporting, and structured incident response planning across development teams.
In-Depth Guidance
The Documentation Developers Trust
From environment hardening to data protection, access our growing library of platform-specific security documentation and reusable templates.
Threat Modeling Templates
Structured models for identifying risks early in the design phase.
Regulatory Compliance Checklists
Guides for maintaining strict regulatory standards (e.g., GDPR, SOC 2).
Ready to Measure Your Security Maturity?
Utilize our self-assessment tools to benchmark your current security processes against industry leaders and identify critical gaps immediately.